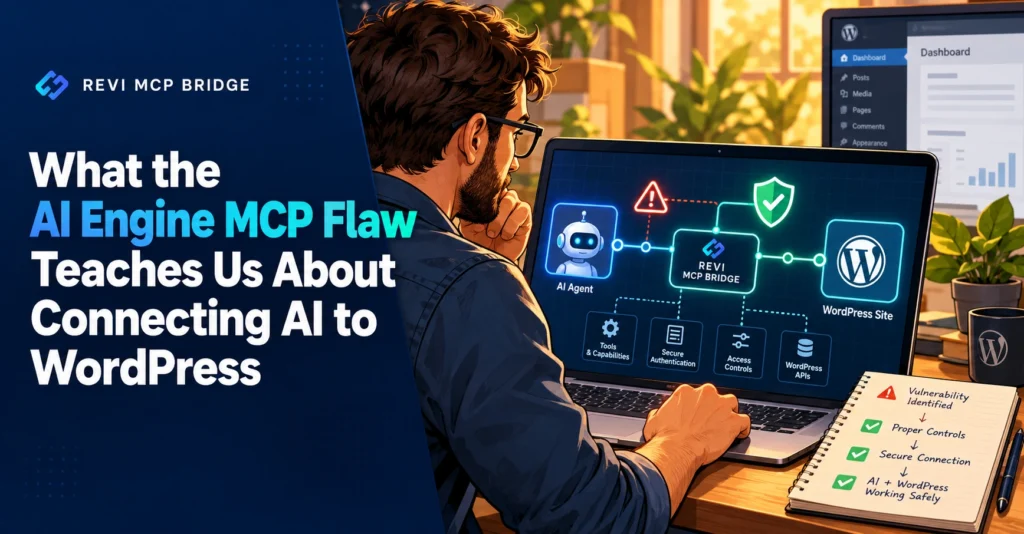
What the AI Engine MCP Flaw Teaches Us About Connecting AI to WordPress
A 2025 vulnerability showed how an MCP connection can become a path to administrator access. The lesson is not to avoid AI. It is to check every call, every time.
Privilege escalation
5 min read
Quick Answer
Security researchers at Wordfence disclosed a critical flaw in the AI Engine WordPress plugin that let authenticated users escalate their privileges to administrator by abusing its MCP feature. Over 100,000 sites were affected and a patch was released on June 18, 2025. The takeaway: an MCP endpoint must check the caller’s permissions on every request, not once at the door.
Who This Is For
Anyone running a WordPress MCP plugin, or thinking about it, who wants to know what to look for before trusting one with the keys.
What Happened
Wordfence reported a vulnerability in the AI Engine plugin, which includes an MCP feature. A logged-in user with low privileges could use that feature to give themselves administrator rights. From there, a takeover of the site is possible. The developer patched it on June 18, 2025.
The details of that case are on Wordfence’s advisory. We cite it here as a lesson, not as a comparison, and we have no inside knowledge of that plugin.
Why MCP Raises the Stakes
An MCP server exposes tools: create a user, edit a file, change a setting. If any one tool skips the “is this person allowed?” check, an attacker gets the power of that tool without needing the account that should have it.
- More tools means more checks to get right. Every tool is a door.
- An AI client is a new caller. It acts on instructions, including ones it should not follow.
- Dangerous tools sit next to harmless ones. Reading a post and creating an admin are one request apart.
Questions to Ask Any MCP Plugin
Is permission checked per call?
Not just at login. Each tool should confirm the caller is allowed to use it.
Can I limit what it can do?
Look for modes or scopes, with a read-only option.
Is there an audit log?
You should be able to see which calls ran, when, and under whose connection.
Can I revoke access fast?
Disconnecting a client should be one click from wp-admin.
How Revi MCP Approaches It
In Revi MCP, every tool call is checked against the site’s active safety mode and its own permission scope before it runs, and nothing bypasses that gate. Calls are logged with who, what and when, secrets redacted, and you can revoke a connection from wp-admin.
That is a design choice, not a guarantee. No plugin can promise it has no bugs, and we do not claim Revi MCP makes a site immune to attack. Keep WordPress, themes and plugins updated, and treat MCP access like any other administrator credential.
See How Revi MCP Limits What AI Can Do
Five safety modes, per-call checks and a full audit log, free on one site.
FAQ
Is MCP itself unsafe on WordPress?
No. The protocol is not the problem. The risk is a plugin that exposes a tool without checking who is calling it.
If I use an AI plugin, what should I do first?
Update it, check its changelog for security fixes, and review who has accounts on your site.
Where can I read the original advisory?
Search for the AI Engine MCP privilege escalation on Wordfence’s vulnerability database for the full technical detail.
Related reading: WordPress MCP server guide · Setup and connection guide · Pricing